HiSecEngine USG6500G Series
AI Firewalls
This site uses cookies. By continuing to browse the site you are agreeing to our use of cookies. Read our privacy policy>


HiSecEngine USG6500G Series AI Firewalls
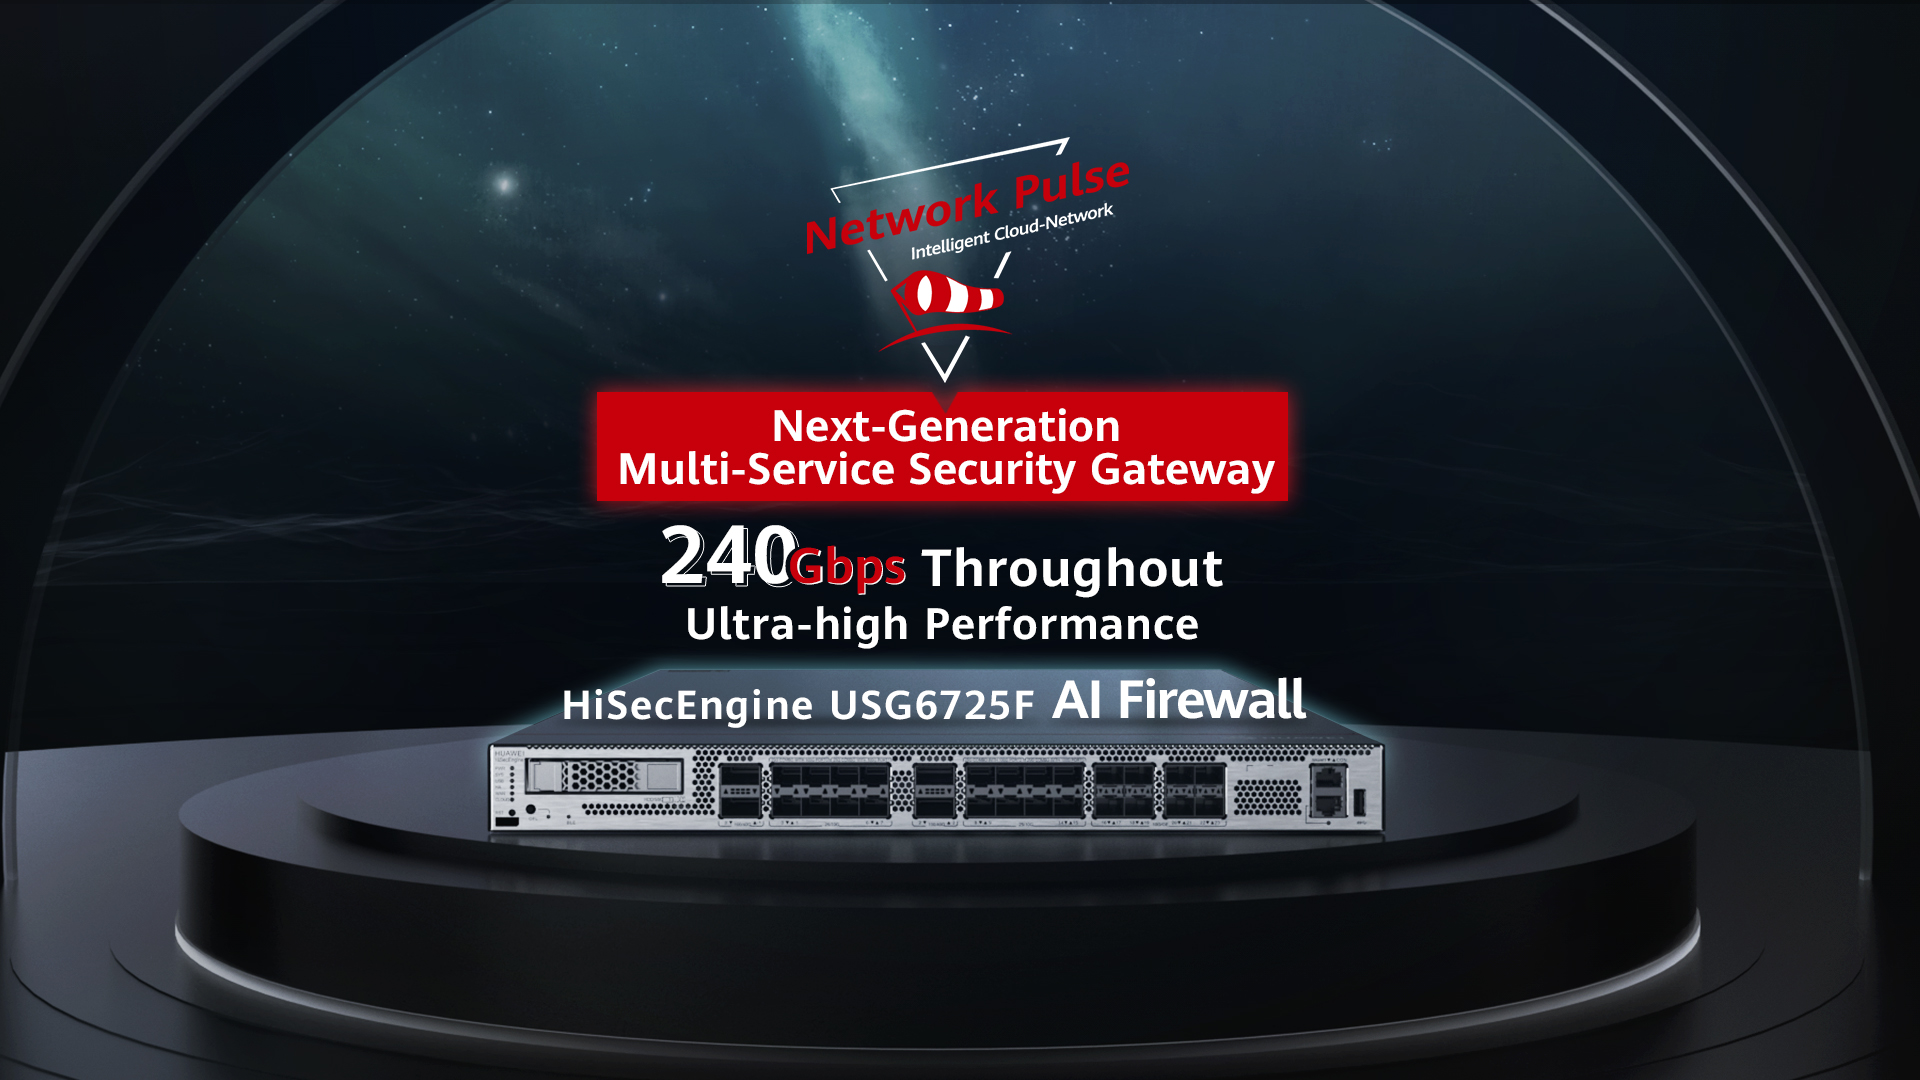
With new hardware and software architectures, The HiSecEngine USG6500G series AI firewalls are next-generation AI firewalls that feature intelligent defense, outstanding performance, and simplified O&M, effectively addressing the preceding challenges. The HiSecEngine USG6500G series AI firewalls use intelligence technologies to enable border defense to accurately block known and unknown threats. Equipped with multiple built-in security-dedicated acceleration engines, The HiSecEngine USG6500G series AI firewalls support enhanced forwarding, content security detection, and IPsec service processing acceleration. The security O&M platform implements unified management and O&M of multiple types of security products, such as firewalls, Anti-DDoS devices, reducing security O&M OPEX. These products are widely used in enterprise branch offices and campus egress border protection.
Huawei Firewalls Continuously Lead Technological Innovation
Ranked in the "Challengers Quadrant" for six consecutive years.
Three Reasons for Choosing Huawei Firewalls

Exceptional Performance
• Adaptive Security Engine (ASE): Dynamically allocates resources across service modules to maximize resource utilization and enhance overall performance.
• NP, pattern matching, and encryption/decryption co-processing engines: Improve small-packet forwarding performance, reduce forwarding latency, and enhance capabilities in application identification, intrusion detection, and services such as IPsec.
Intelligent Defense
• Hundreds of millions of virus samples: The AI-powered Content-based Detection Engine (CDE) covers a vast database of virus samples, effectively defending against virus attacks.
• AI security detection algorithm: AI detection algorithms are deployed at local gateways, enabling deep analysis of malicious behavior. This allows rapid identification of unknown virus variants, achieving a 95% detection rate for unknown threats.
Simplified O&M
• Unified O&M: A centralized controller enables unified policy orchestration and automated alarm correlation analysis. Combined with cloud-network-edge coordination, it enables threat response within seconds.
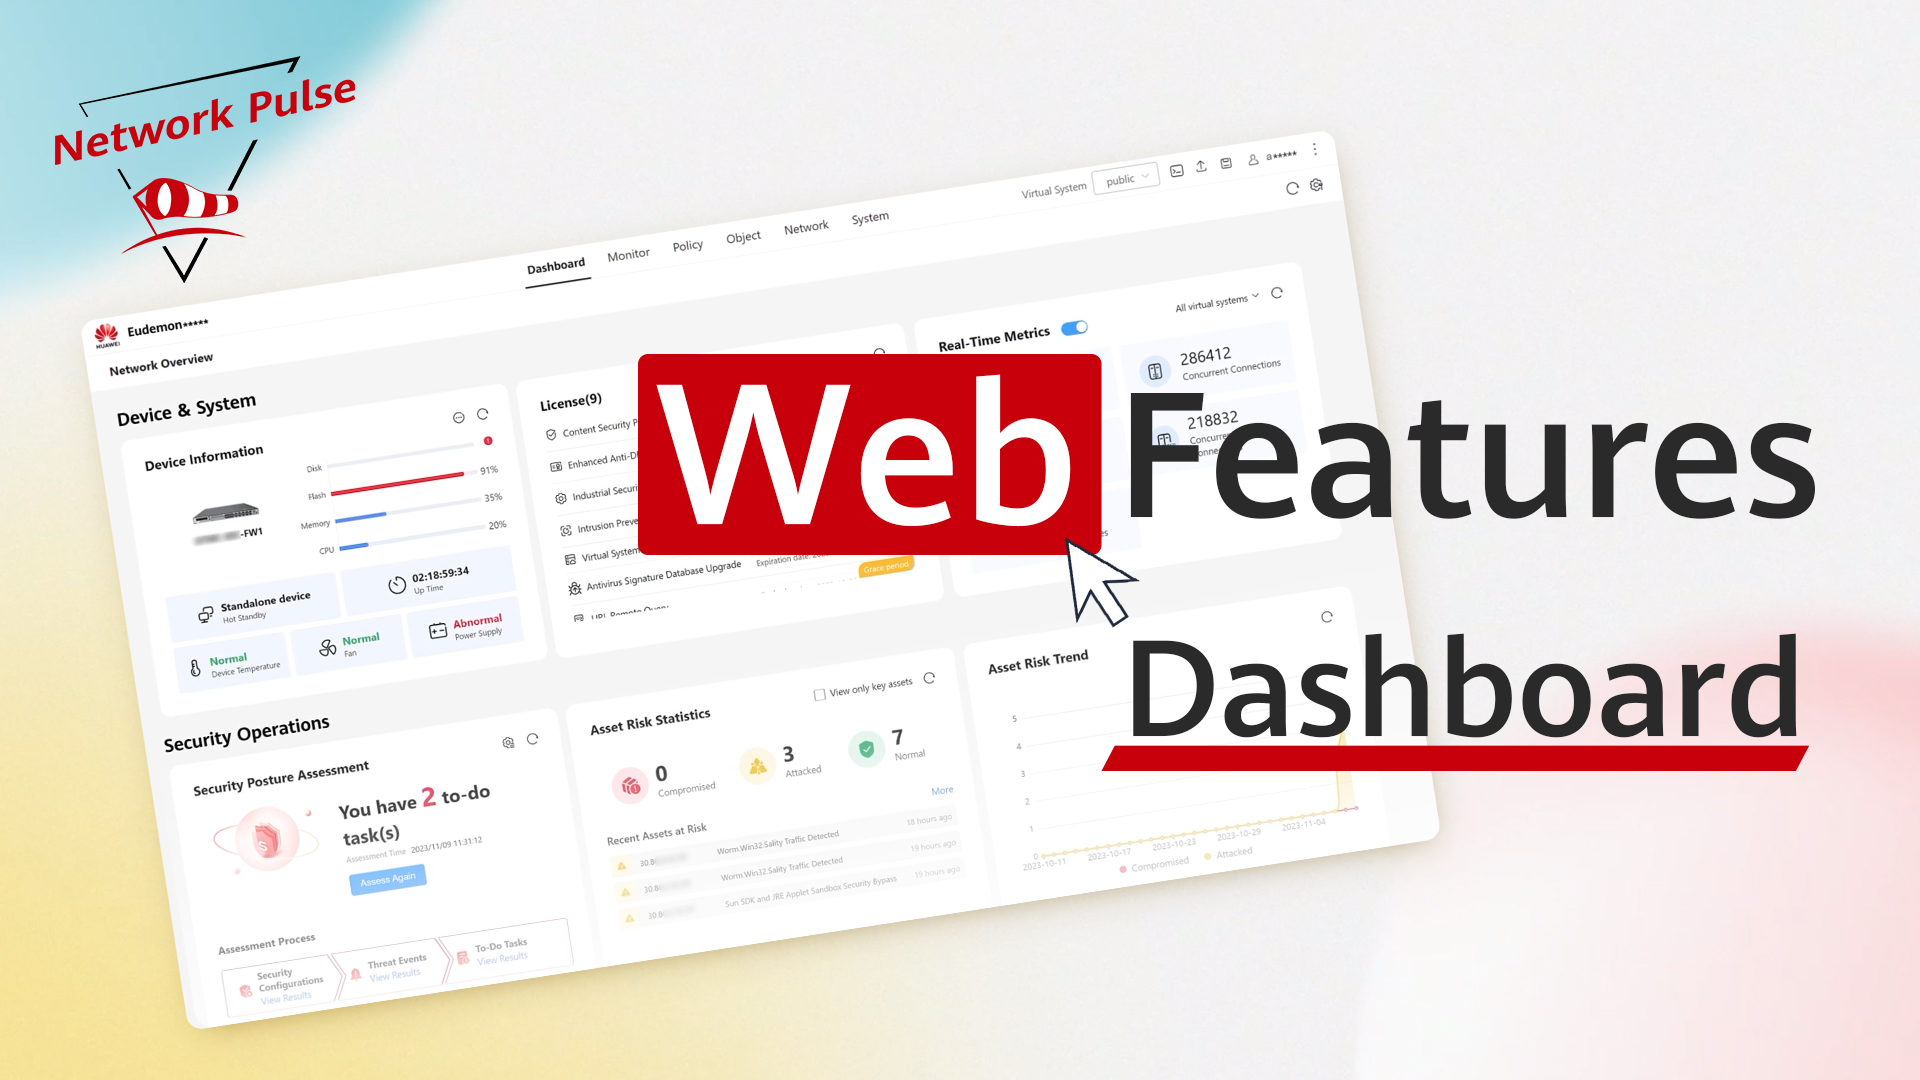
• Simplified O&M: A newly defined security interface with threat visualization presents key information, such as device status, alarms, traffic, and threat events in an intuitive way, simplifying O&M.
Specifications
| Parameters | USG6505G-D | USG6550G-D USG6550G-DP |
USG6550G-D5G USG6550G-DP5G |
USG6570G-D | USG6590G-D |
| Fixed ports | 4*GE RJ45+1*GE SFP | 4*GE RJ45+2*2.5GE RJ45+2*10GE (SFP+) | 4*GE RJ45+2*2.5GE RJ45+2*10GE (SFP+),Support 5G | 12*GE RJ45+4*10GE (SFP+) | 12*GE RJ45+4*10GE (SFP+) |
| Form factor | Desktop model | ||||
| Dimensions(W×D×H)mm | 320mm×210mm×43.6mm | ||||
| Integrated protection | Integrates firewall, VPN, intrusion prevention, antivirus, bandwidth management, Anti-DDoS, URL filtering; provides a global configuration view; manages policies in a unified manner. | ||||
| Application identification and control | Identifies over 6000 applications and supports the access control granularity down to application functions; combines application identification with intrusion detection, antivirus, and data filtering, improving detection performance and accuracy. | ||||
| Intrusion prevention and web protection | Obtains the latest threat information in a timely manner for accurate detection and defense against vulnerability-based attacks. Supports coverage of tens of thousands of Common Vulnerabilities and Exposures (CVE). Detects malicious traffic, such as vulnerability attack traffic, web attack traffic (such as SQL injection and cross-site scripting attacks), botnets, remote control, and Trojan horses, and supports brute-force attack detection. Supports 13,000+ IPS signatures, and supports user-defined signatures. The default IPS blocking rate is up to 85%. Supports brute-force cracking detection based on user behaviors, and user-defined statistical periods. | ||||
| Antivirus | Supports intelligent, heuristic antivirus engine that can detect hundreds of millions of virus variants. And supports the detection of files compressed in 100 layers. | ||||
| Bandwidth management | Manages per-user and per-IP bandwidth based on service application identification, ensuring the network experience of key services and users. The management and control can be implemented by limiting the maximum bandwidth, guaranteeing the minimum bandwidth, and changing the application forwarding priority. | ||||
| URL filtering | Provides a URL category database with over 560 million URLs and accelerates access to specific categories of websites, improving access experience of high-priority websites. Supports DNS filtering, in which accessed web pages are filtered based on domain names. Supports the anti-phishing URL filter. |
||||
| Intelligent uplink selection | Supports service-specific PBR and intelligent uplink selection based on multiple load balancing algorithms (for example, based on bandwidth ratio and link health status) in multi-egress scenarios. | ||||
| VPN encryption | Supports multiple highly available VPN features, such as IPsec VPN, SSL VPN and GRE. | ||||
| Asset management | Provides asset-based threat visualization, which supports associating IPS and Antivirus threat logs with user assets and displaying asset risk assessment results. | ||||
Voices of Customers

★★★★★
Huawei Firewall: Highly Reliable Intelligent Gateway What attracts us most is the high reliability of Huawei's USG series firewalls. These firewalls feature redundant power modules and fans, support hot-swapping, and utilize a dual-node cluster deployment model to ensure the high reliability of IPsec VPN tunnels.
— Director of a Municipal Government Network Department
★★★★★
Huawei Firewall: Intelligent URL Filtering Huawei's USG firewall has been the best choice so far. Its built-in URL filtering feature covers over 500 million URLs, ensuring a safe and healthy Internet experience for both teachers and students.
— Director of the Information Center, a University
★★★★★
Huawei Firewall: Real-Time Advanced Threat Protection We prioritize the detection performance of firewalls. Huawei's USG firewall delivers a very high threat detection rate with minimal false alarms, significantly reducing operational workload.
— O&M Lead, IT Department, a Bank
★★★★★
Huawei Firewall: Unified Security Gateway Huawei's USG integrates SRv6, zero trust, and firewall capabilities into a single solution. The Huawei USG firewall offers powerful advantages and outstanding performance, ensuring secure and stable operation of the entire manufacturing system, from network access to production data transmission.
— IT Manager, a Manufacturing Enterprise
★★★★★
Huawei Firewall: Efficient Virus Detection and Easy-to-Manage Security GatewayHuawei's USG firewall is quick to deploy and easy to maintain. It effectively blocks network intrusions and safeguards core business systems. Its visualized operations and dynamic defense features are highly practical, significantly boosting our security operations efficiency. — Director of the Information Center, an Energy Enterprise
News and Events
Resources
Carregar Mais
Technical Support
Copyright © 2026 Huawei Technologies Co., Ltd. All rights reserved.